IBM Langflow CVE-2026-9198 Allows Unauthenticated RCE
What happened
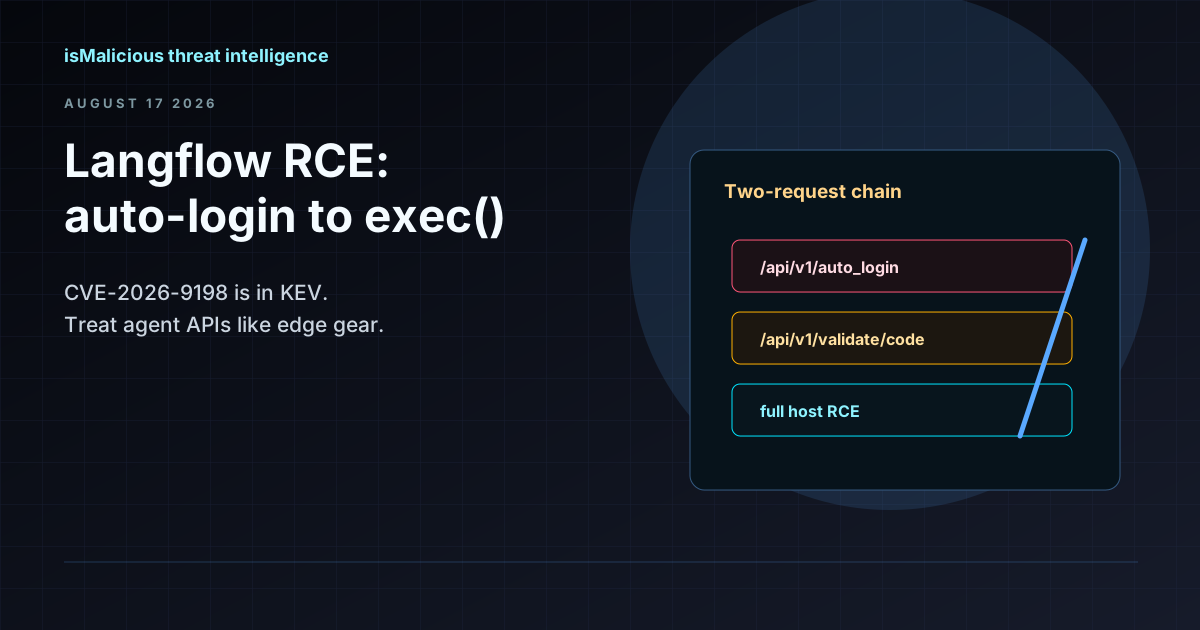
IBM Langflow versions 1.0.0 through 1.10.0 contain a CVSS 9.8 unauthenticated RCE flaw (CVE-2026-9198). The vulnerability allows attackers to obtain a SUPERUSER token via `/api/v1/auto_login` without validation and execute attacker-supplied Python via `/api/v1/validate/code`. IBM released version 1.10.1 to fix the issue. CISA added the CVE to the KEV catalog on 4 August 2026 with a federal remediation deadline of 7 August.
Why it matters
Langflow functions as a remote admin console for LLM workflows and agent graphs, often storing sensitive API keys. An attacker gaining RCE can read environment variables, modify flows to exfiltrate data, and use the host as an egress point. CISA's three-day federal deadline signals immediate risk. Administrators must upgrade to 1.10.1, set `LANGFLOW_AUTO_LOGIN=false`, and restrict network access.
Notes
None
Sources
ismalicious.com · Published: Aug 17, 2026, 8:00 AM